We evaluate your environment, identify gaps, and define exactly what’s needed to meet certification requirements—SOC 2, ISO 27001, HIPAA, FedRAMP, and more.
Stay In The Loop
Subscribe to our weekly emails to stay up to date.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
September 17, 2026
What Is an ISMS, and Why Do Auditors Care?
This article explains the ISMS definition, why auditors care, and what the evidence looks like in practice.
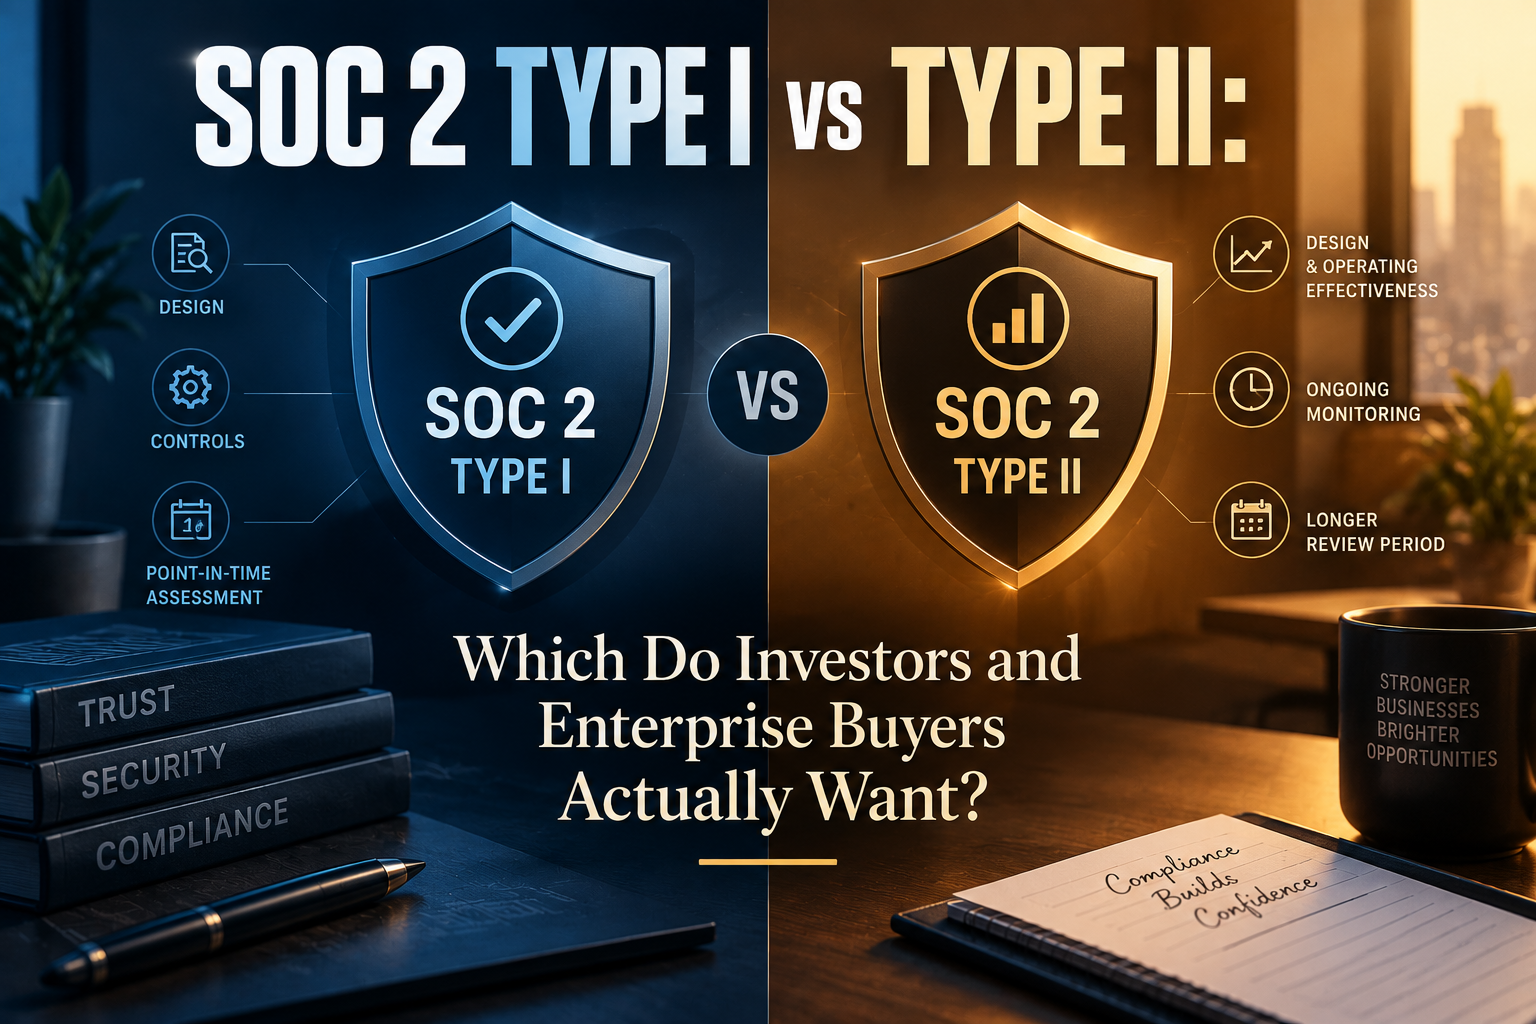
SOC 2 Type I vs Type II: Which Do Investors and Enterprise Buyers Actually Want?
This guide explains the differences between SOC2 Type 1 vs Type 2 , defines what investors and enterprise buyers are looking for, and helps you decide which option is best for your business.