About
Services
Overview
Readiness Evaluation
vCISO Leadership
Third-Party & Partner Assessments
Founder
Blog
Contact
BrightLine Insights: Real-World Compliance Clarity
Most compliance advice is either too generic or buried in jargon. BrightLine Insights delivers clear, actionable guidance on certifications, audits, and security controls that actually work.
September 17, 2026
What Is an ISMS, and Why Do Auditors Care?
This article explains the ISMS definition, why auditors care, and what the evidence looks like in practice.
August 25, 2026
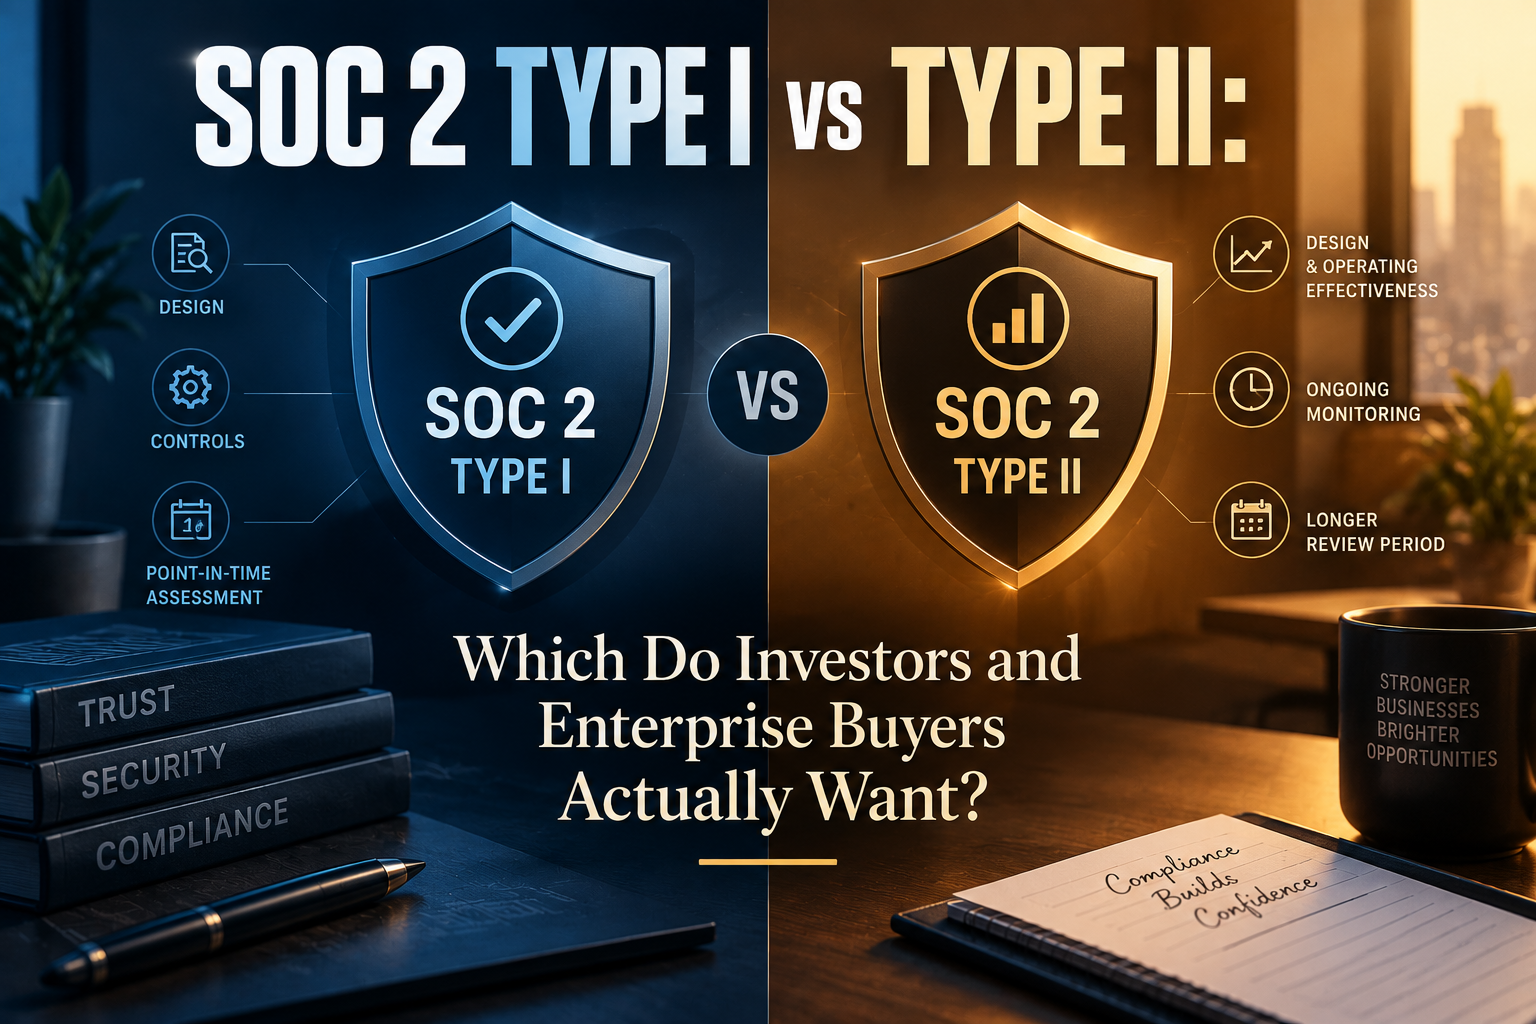
SOC 2 Type I vs Type II: Which Do Investors and Enterprise Buyers Actually Want?
This guide explains the differences between SOC2 Type 1 vs Type 2 , defines what investors and enterprise buyers are looking for, and helps you decide which option is best for your business.
August 19, 2026
ISO 27001 for U.S. Companies: Why International Clients Are Asking for It
How BrightLine Helps U.S. Companies Become ISO 27001-Ready
May 29, 2026
SOC 2 Readiness: What Auditors Really Look For
We evaluate your environment, identify gaps, and define exactly what’s needed to meet certification requirements—SOC 2, ISO 27001, HIPAA, FedRAMP, and more.
May 29, 2026
Building a Million-Dollar Influencer Program: Lessons from Lily Comba
We evaluate your environment, identify gaps, and define exactly what’s needed to meet certification requirements—SOC 2, ISO 27001, HIPAA, FedRAMP, and more.
Let’s Talk About
Strengthening
Your Security Posture
Schedule a 30‑minute conversation. No pitch, no pressure.
Let’s Talk
© 2026 Brightline. All rights reserved.